New Guide 'Cybersecurity Frameworks: What K-12 Leaders Need to Know' Released by K12SIX, SETDA
- By Kristal Kuykendall
- 10/20/22
The national nonprofit cybersecurity advocacy group for public schools, K12 Security Information Exchange, has released a new guide for state and local K–12 education leaders, “Cybersecurity Frameworks: What K–12 Leaders Need to Know,” which urges the adoption of cybersecurity best practices at the local and state levels of public education.
The guide was commissioned by the State Educational Technology Directors Association as part of its Cybersecurity & Privacy Collaborative and funded by the Bill & Melinda Gates Foundation, according to a news release.
K12SIX noted that although “there is no shortage of advice” for organizations to improve their cybersecurity defenses, “little of that advice reflects the context in which schools work or addresses the unique challenges and constraints facing the K–12 education sector.”
The new K12SIX guide aims specifically to “help education leaders to understand the purpose and structure of common cybersecurity best practice frameworks, understand the similarities and differences among these frameworks, and encourage the growth in cybersecurity framework adoption by school systems nationwide.”
The guide, which is free to download at the Open Educational Resources Commons website, provides an overview of the three primary frameworks used by and recommended for schools, and explains the differences and similarities between the three — in layman’s terms to empower district and state education leaders to select their schools’ best path for cybersecurity planning. It then dives deeper into each of the three frameworks, explaining what each entails.
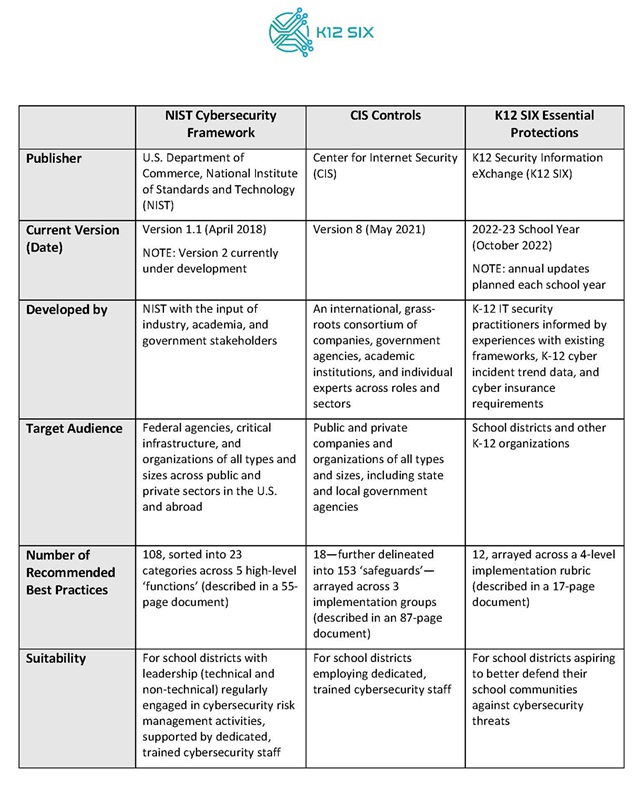
“The growth in both the frequency and severity of school cyber incidents begs the question of what school leaders need to know and do to defend their school systems better,” said K12SIX National Director Doug Levin. “Cybersecurity frameworks, which are compilations of cost-effective best practice advice, offer a common-sense way for K–12 leaders to prioritize scarce time and resources in guarding against the growing array of cyber threats facing schools.”
“This thoughtful analysis of best-practice frameworks is another example of the practical, school-focused guidance K12SIX delivers for our states and districts. SETDA appreciates Doug Levin’s expertise in helping schools develop better practices for cybersecurity risk management,” said Jason Bailey, Director of Innovation and Design at SETDA.
K12SIX emphasized the importance of adopting a cybersecurity framework in educational institutions’ efforts to effectively mitigate and manage schools’ cybersecurity risks, as ransomware attacks targeting public school systems continue to grow in frequency and severity.
The guide encourages education leaders to:
- Commit to improving K-12 cybersecurity defenses by adopting a cybersecurity framework as a management and communication tool
- Consider the capacity of their school system before choosing which framework to adopt
- Understand that cybersecurity framework implementation requires flexibility
Download “Cybersecurity Frameworks: What K-12 Leaders Need to Know” at the OER Commons site. Find additional K–12 cybersecurity resources at K12SIX.org or SETDA.info.
About the Author
Kristal Kuykendall is editor, 1105 Media Education Group. She can
be reached at [email protected].